Security7 min read
Static permissions judge each AI agent action alone. Dynamic safeguards react to what the agent already did in the session, so you can say yes to agents on sensitive data.
Security4 min read
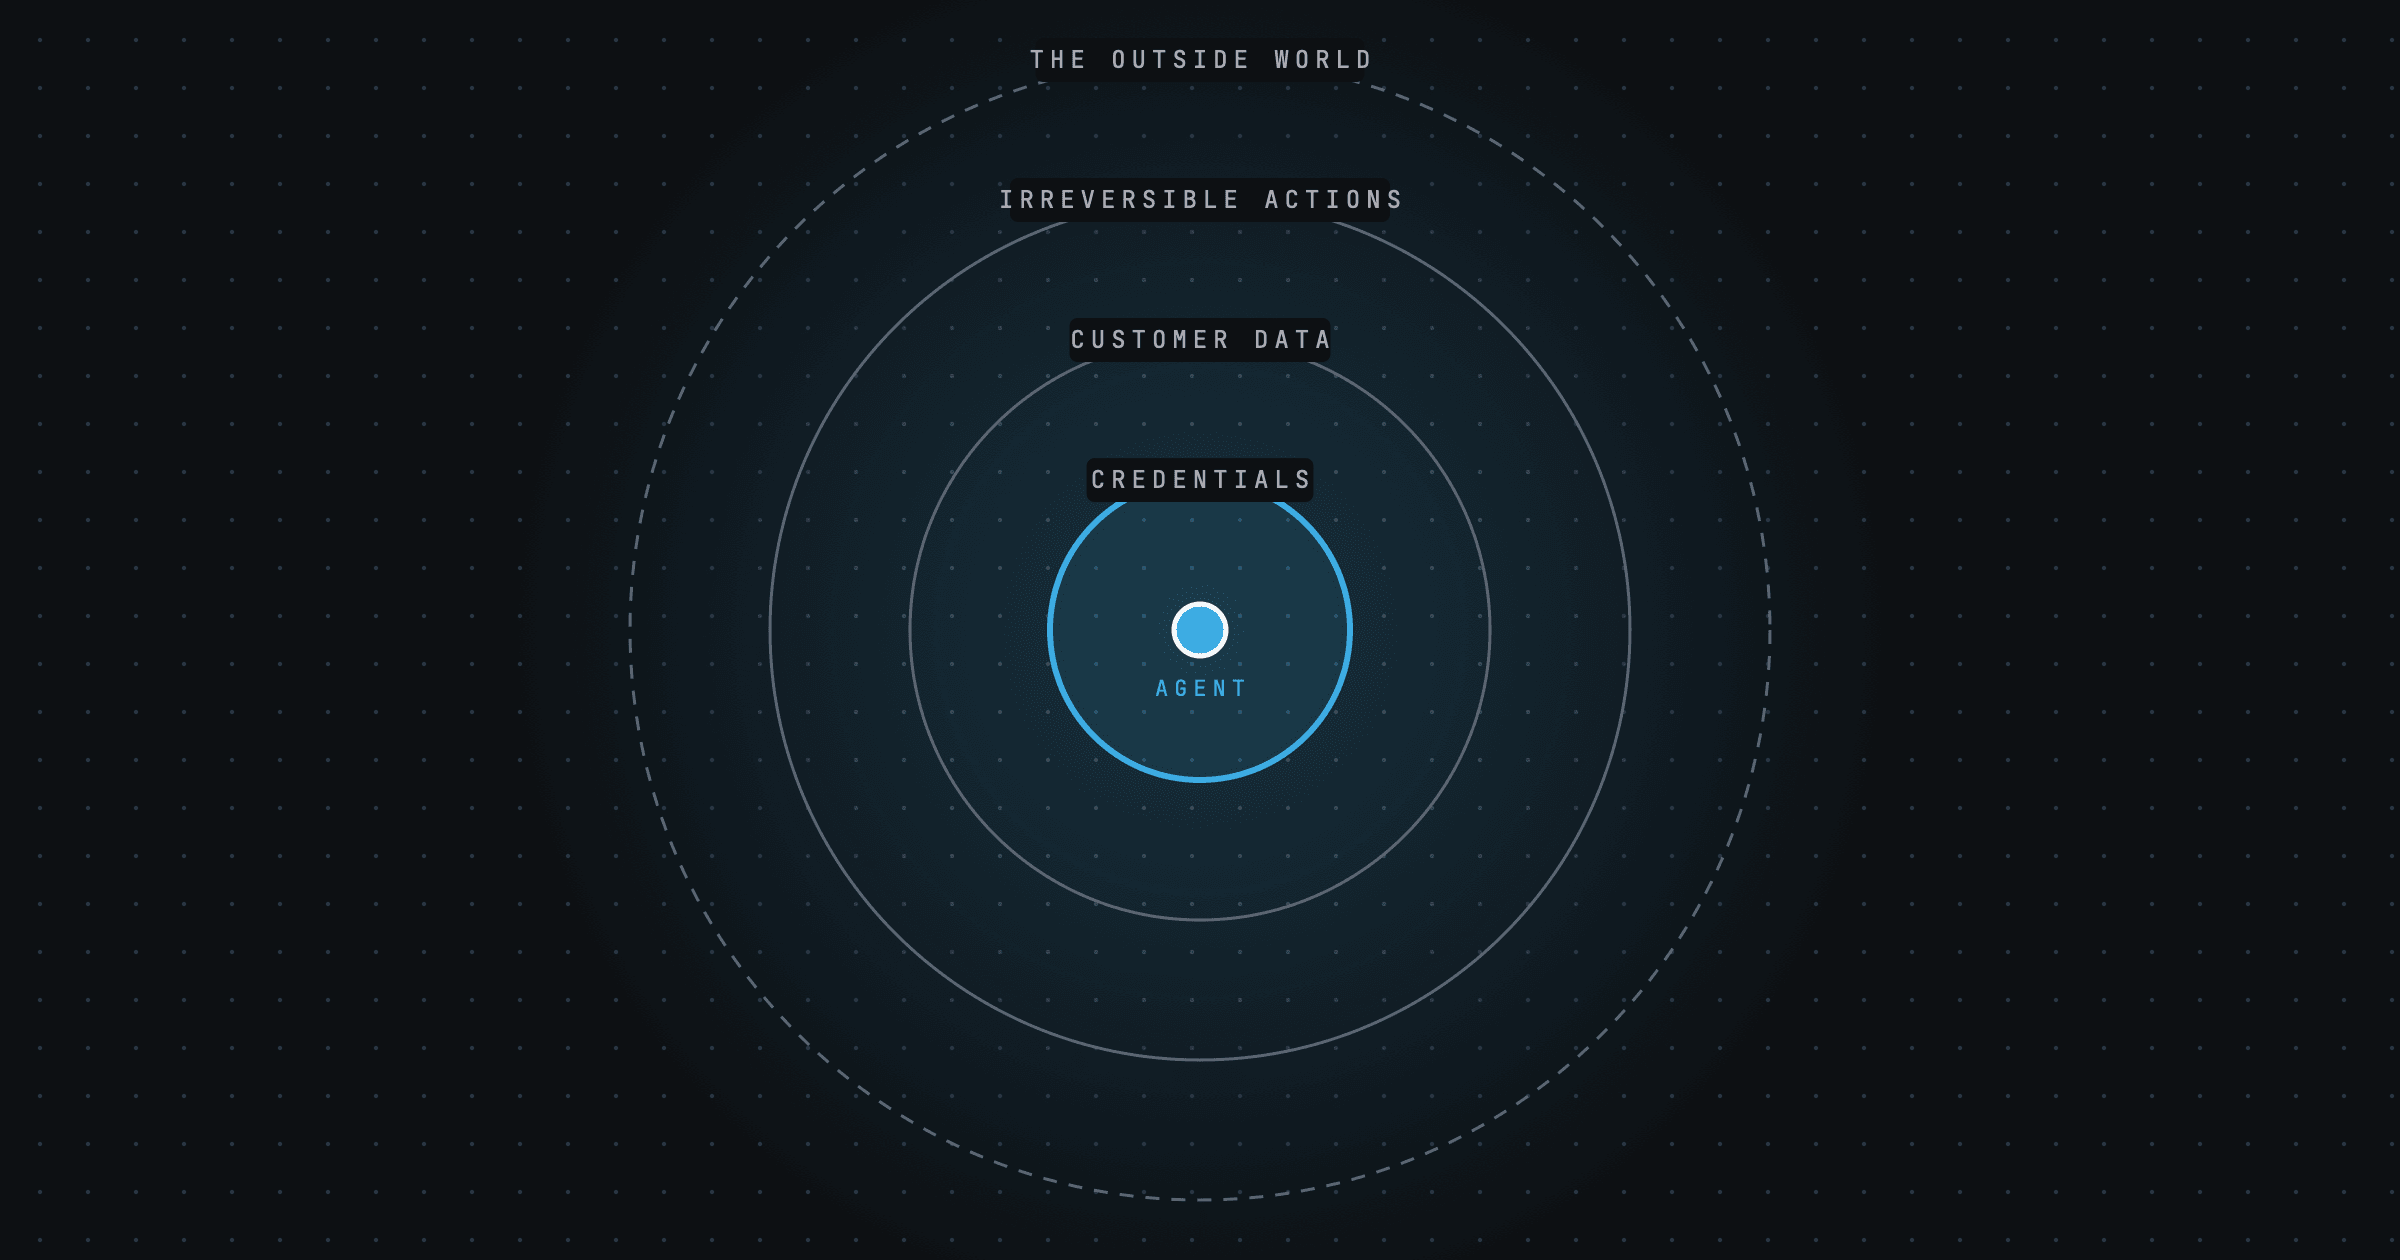
Of all the questions to ask before handing an AI agent access to your systems, one does most of the work: if this goes wrong, what is the worst that can happen? Four versions of that question, and how to act on the answers.
Security7 min read
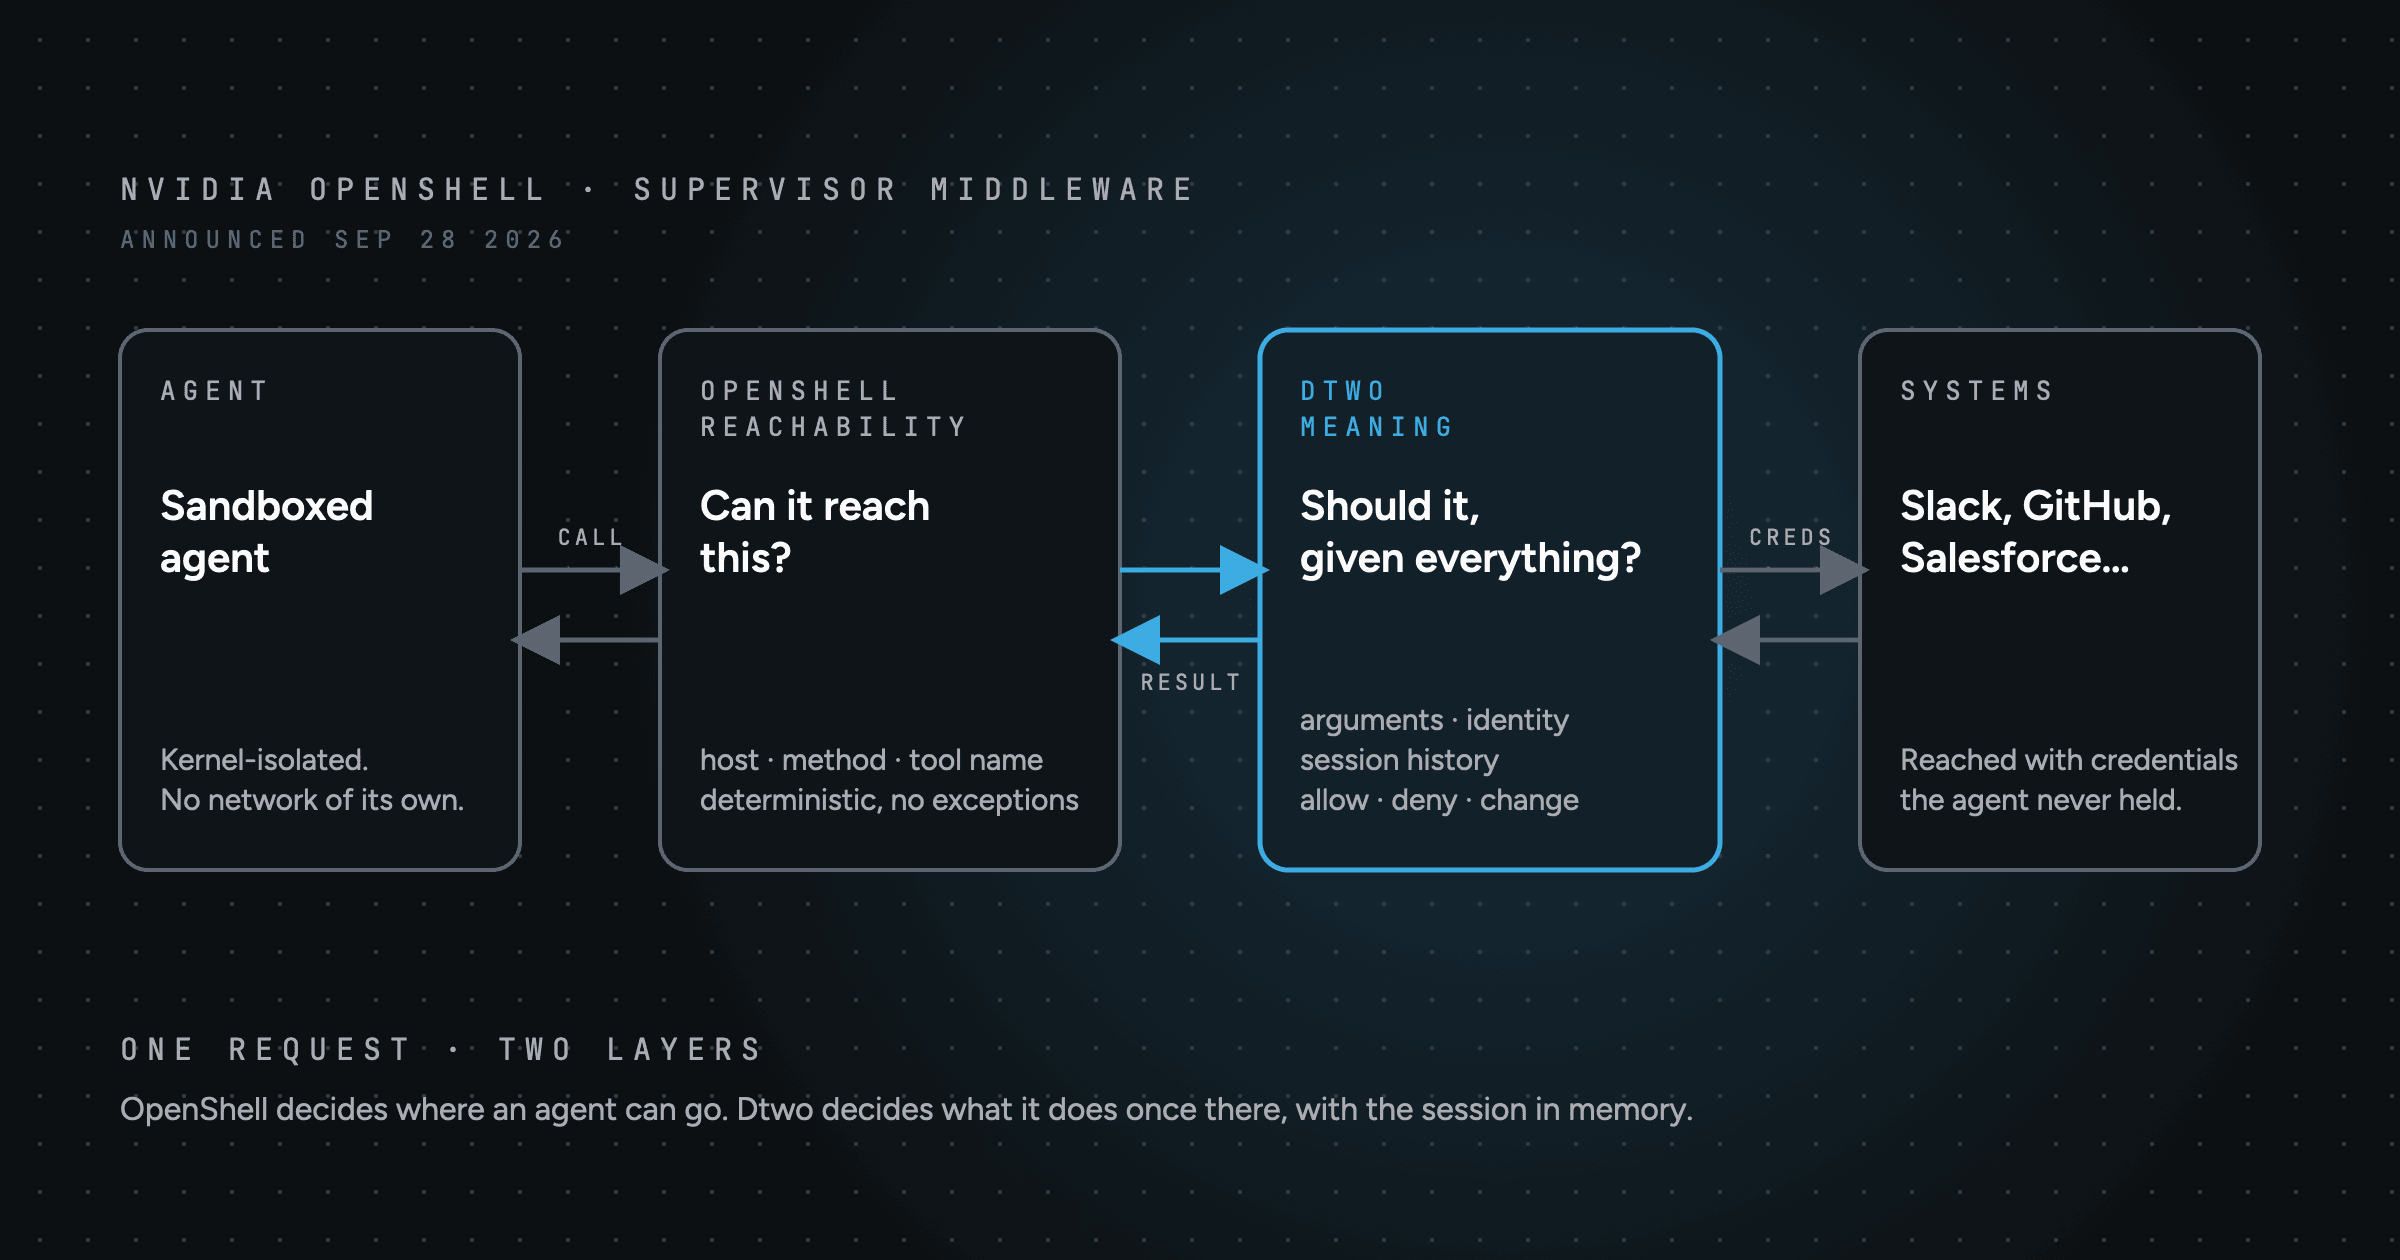
NVIDIA's OpenShell, announced September 28, decides what an agent can reach. Dtwo sits in its middleware hook and judges each call by its arguments and by what the session already did elsewhere. If you run agents in OpenShell, you still need that layer.
Security6 min read
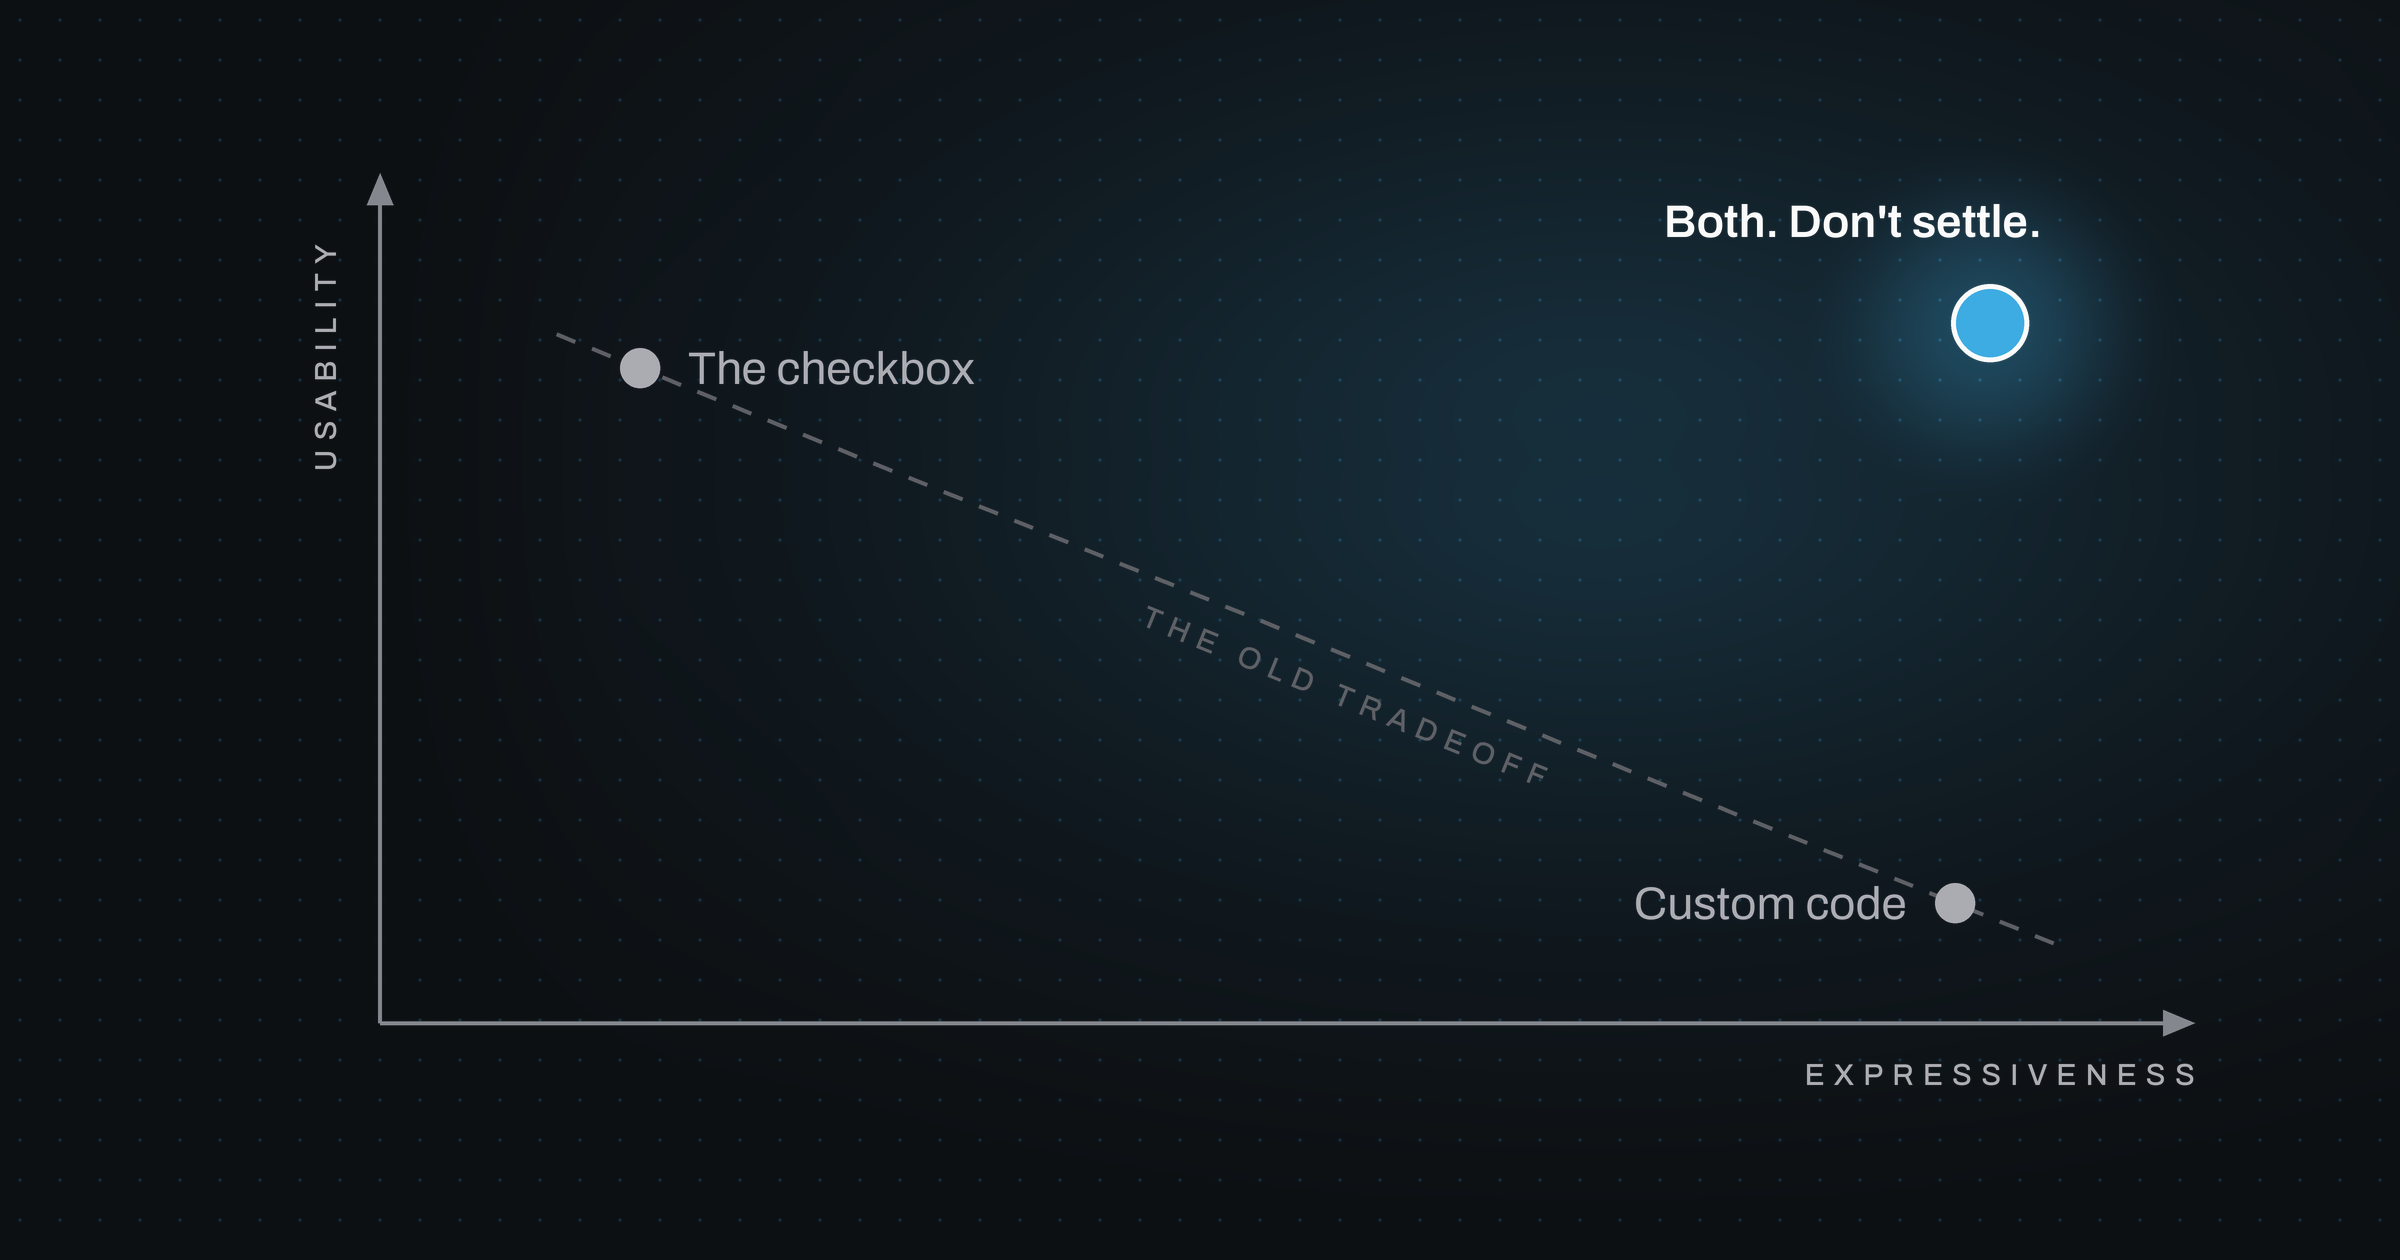
Expressiveness and usability. Everything else on the vendor's feature list is one of those two in disguise.
Security6 min read
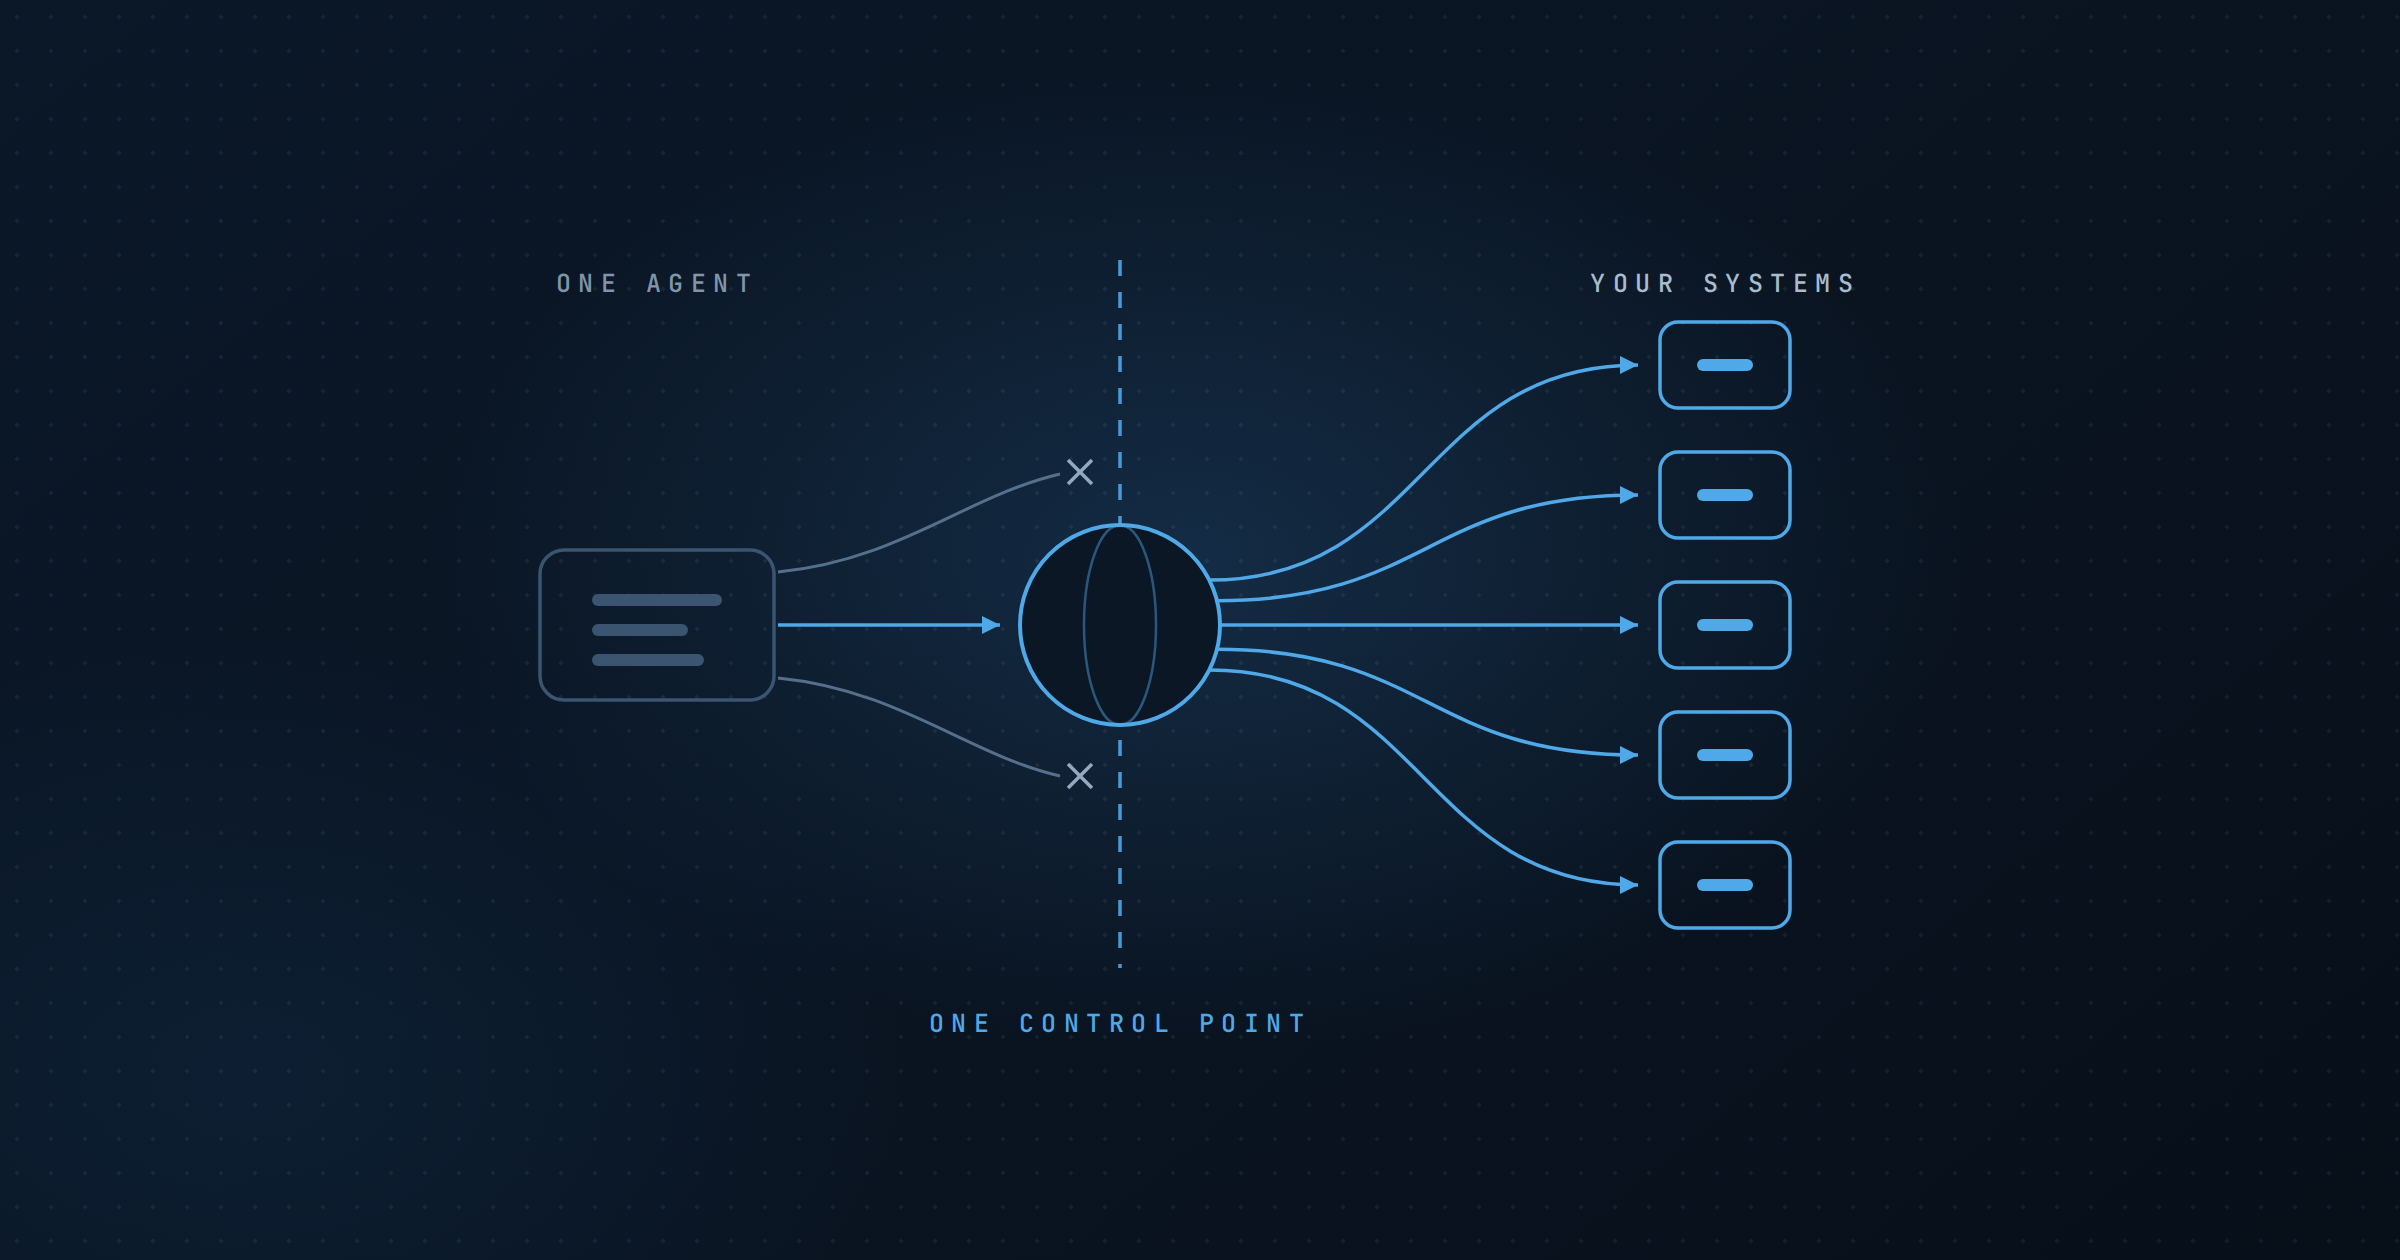
Our founding AE runs his entire sales job through Dtwo — prospecting, CRM, call prep, follow-up — and explains what a single control point actually buys you.
Security3 min read
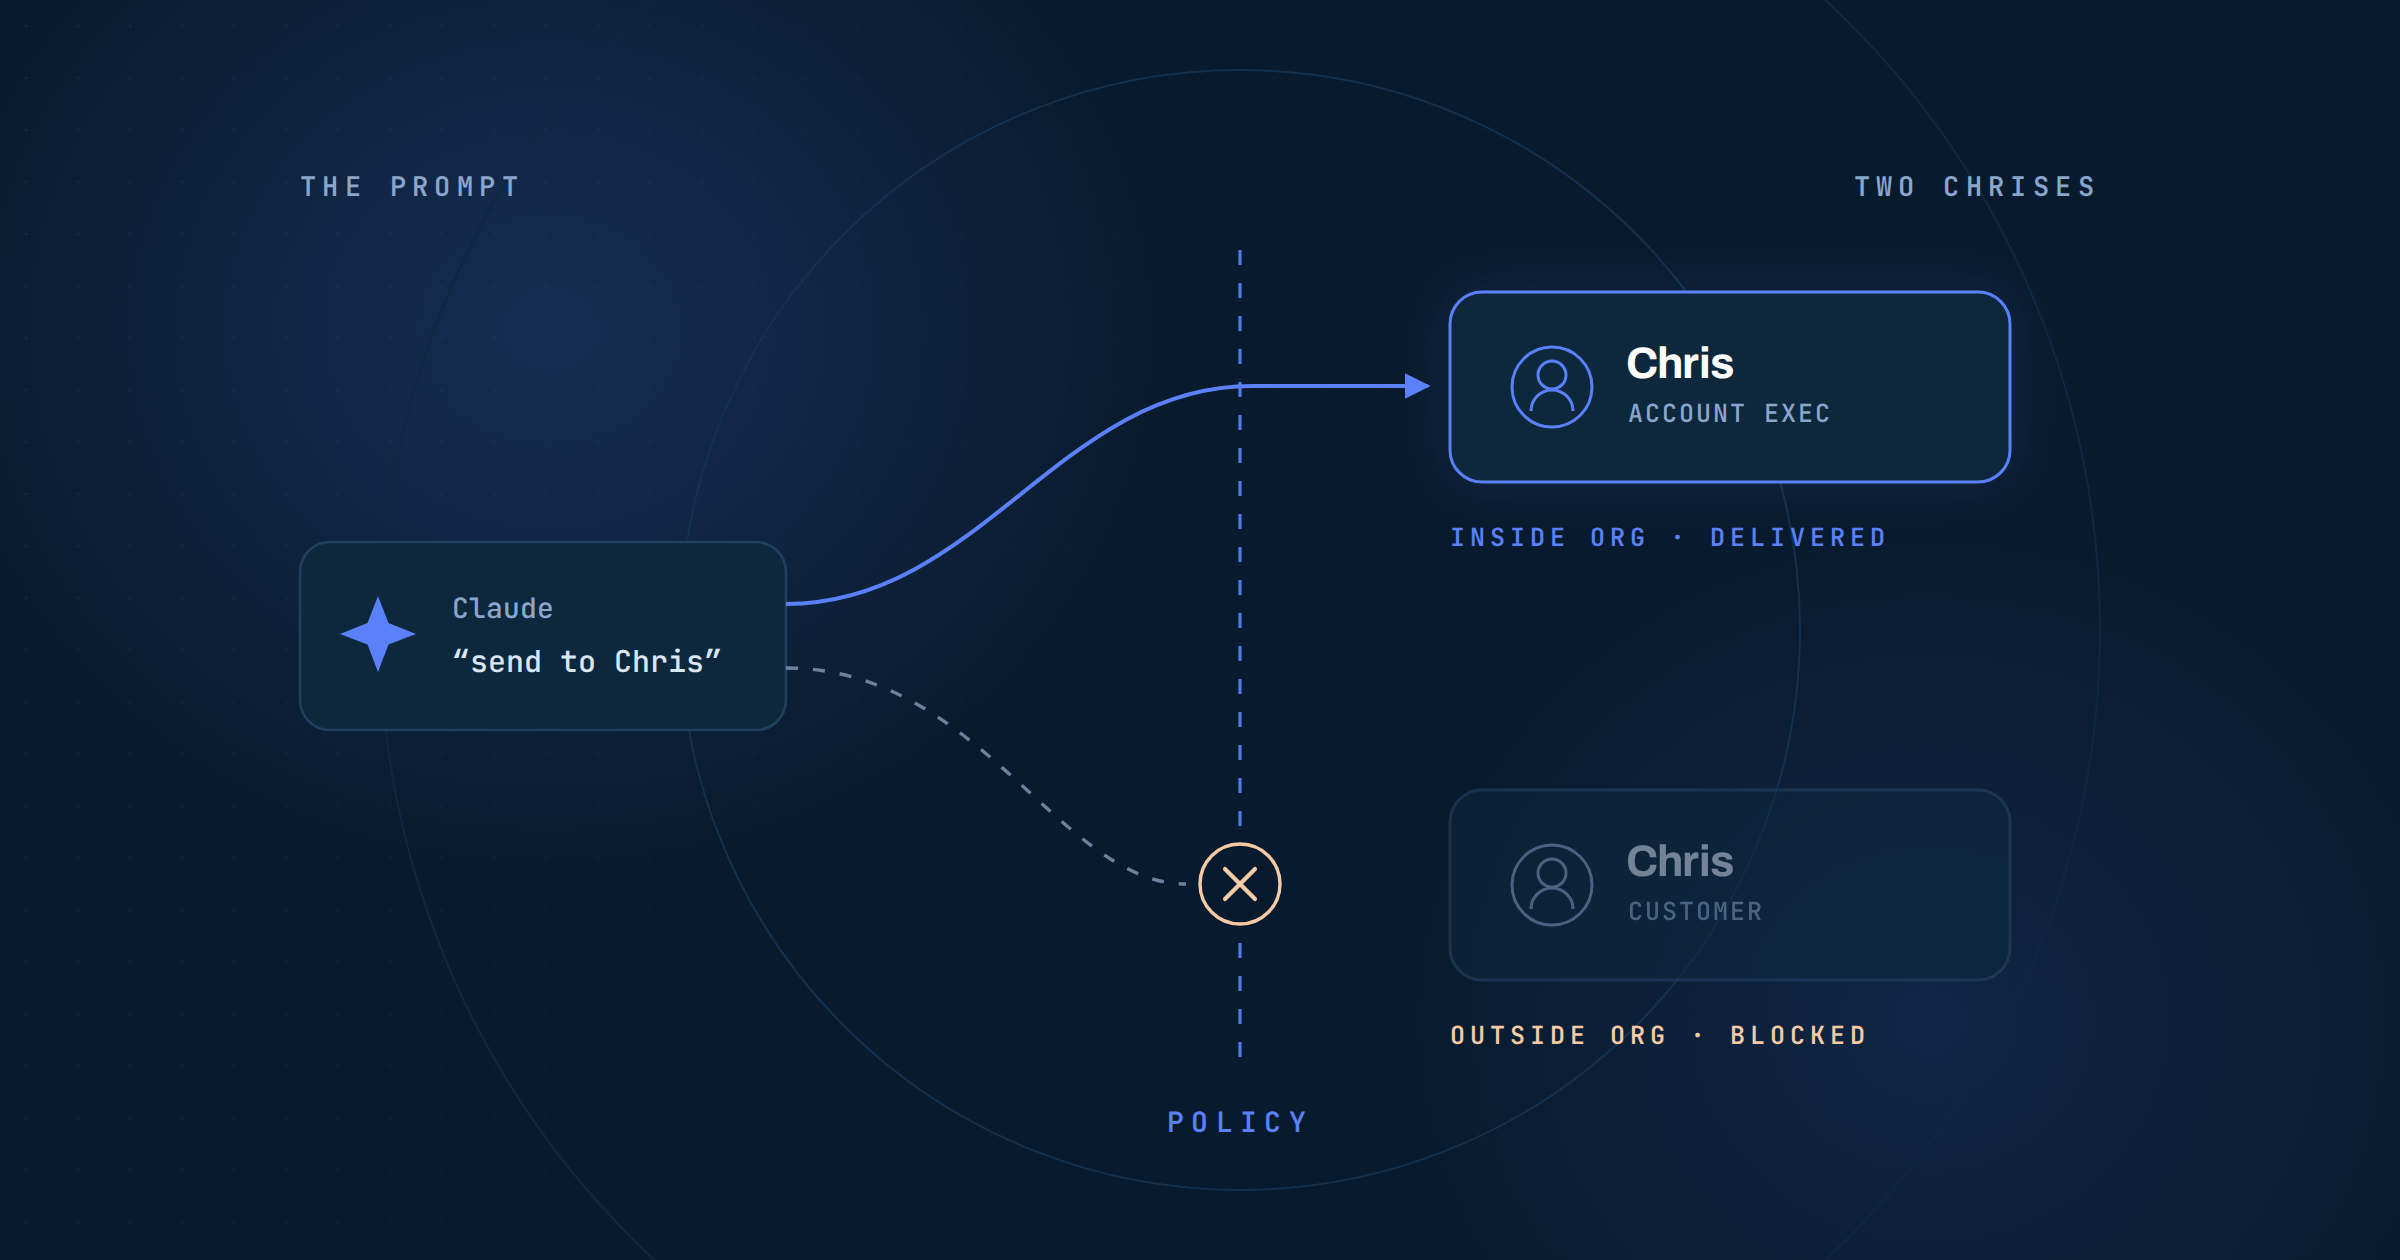
There are two Chrises in our Slack — a coworker and a customer. Here's the policy I wrote so an agent picking the wrong one can't turn into a data breach, and what I learned when a policy went too far the other way.
Security3 min read
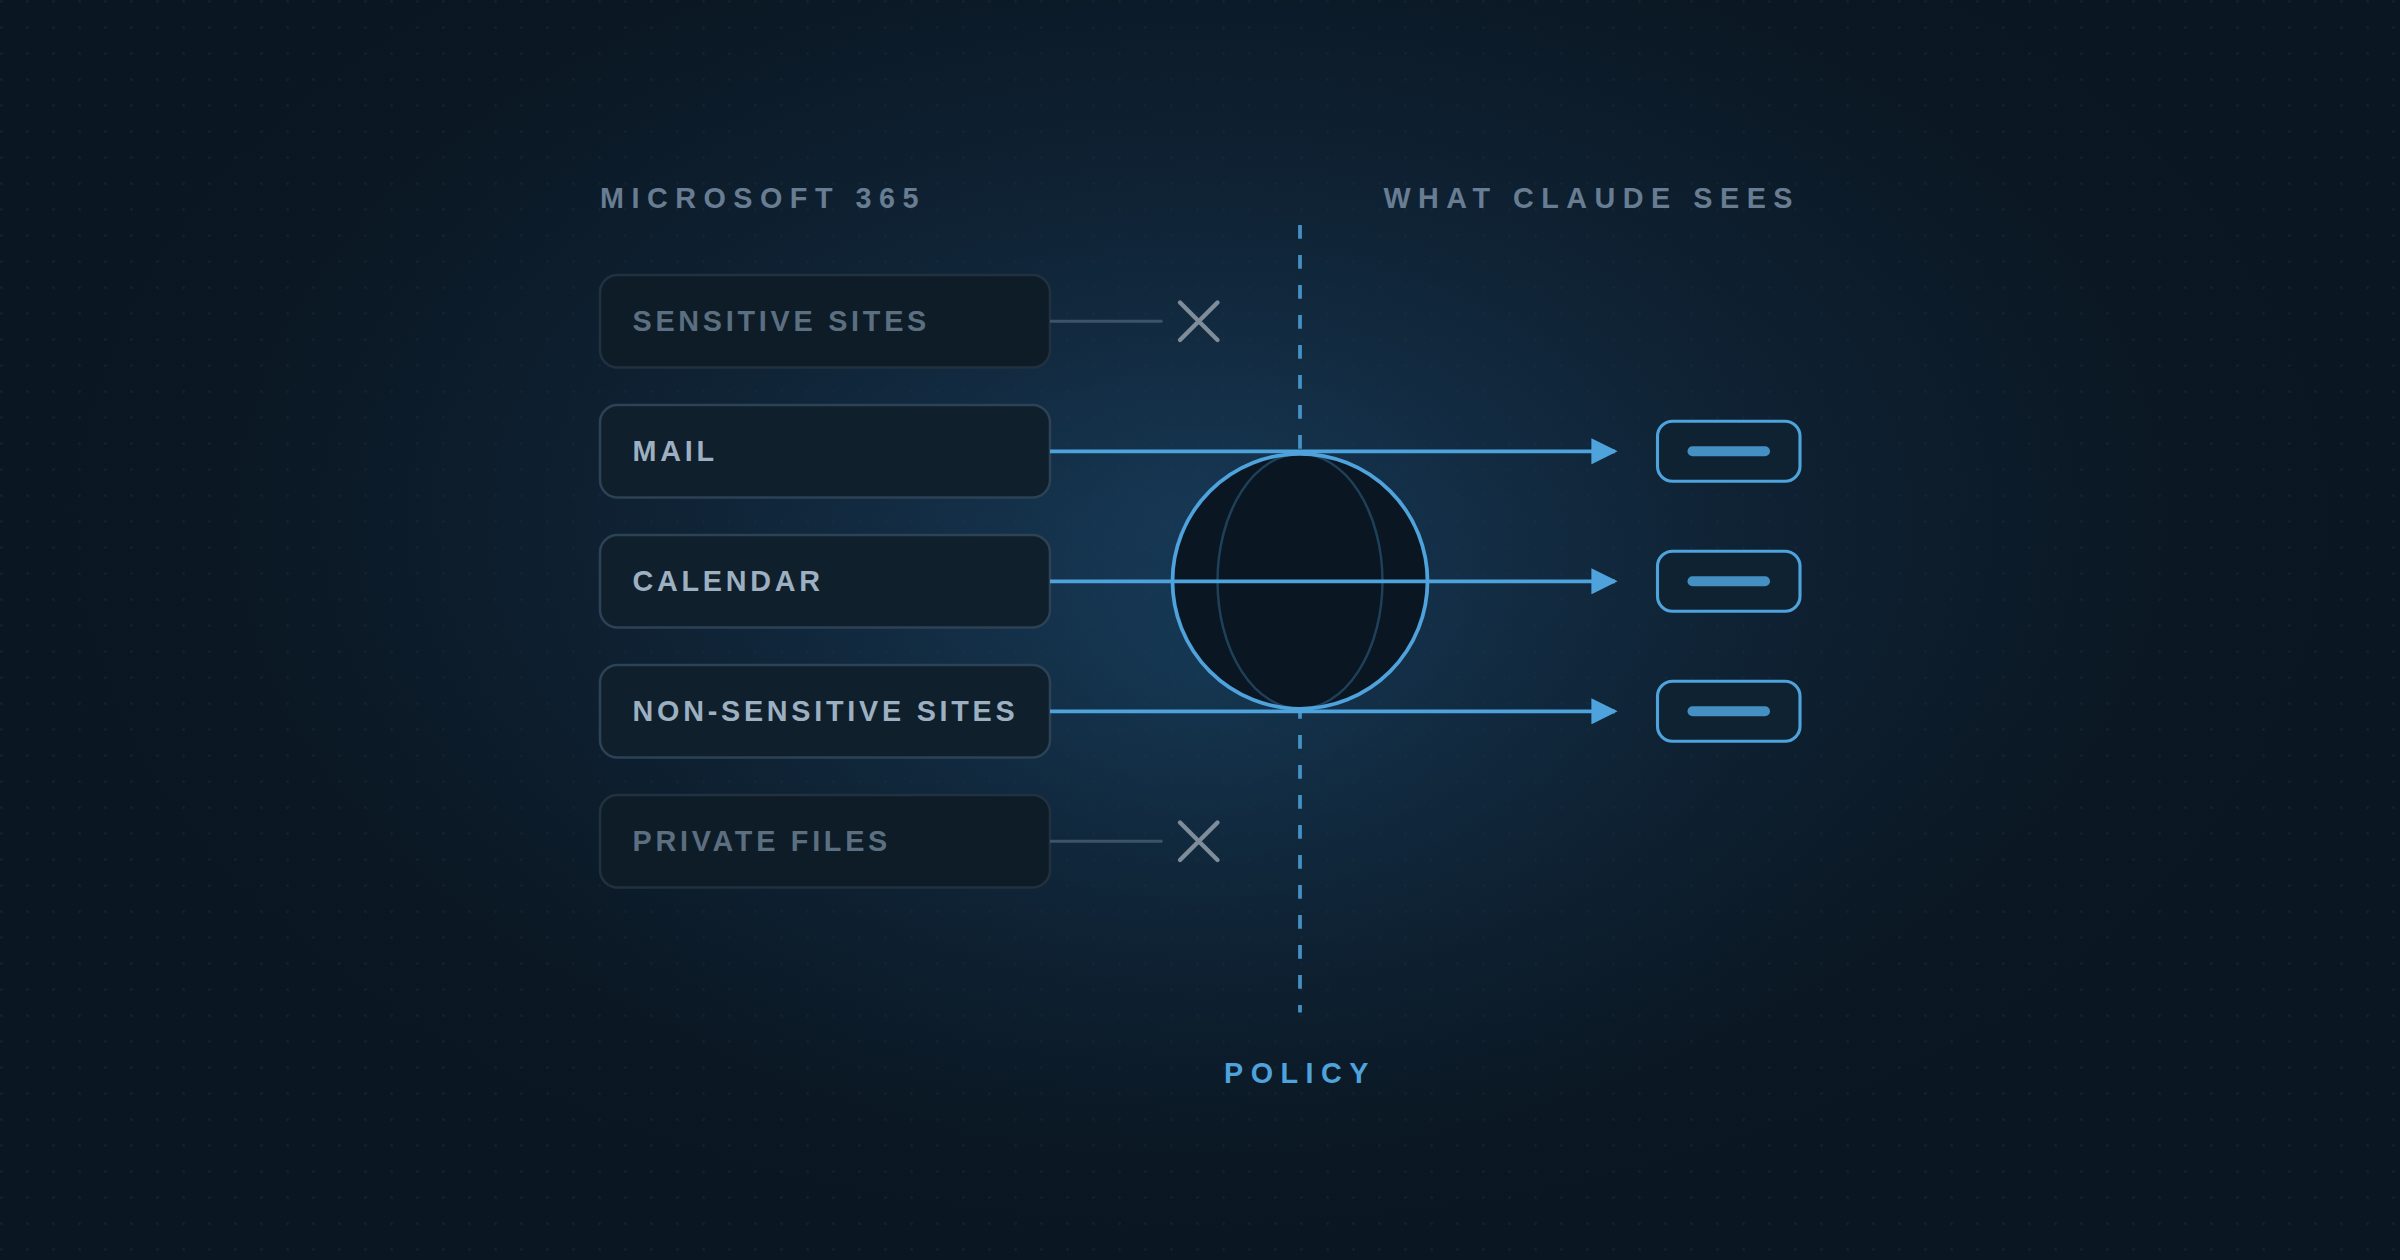
Security teams keep saying no when users ask to connect Claude to email. The problem isn't access, it's granularity. Here's what a yes can look like.
Security5 min read
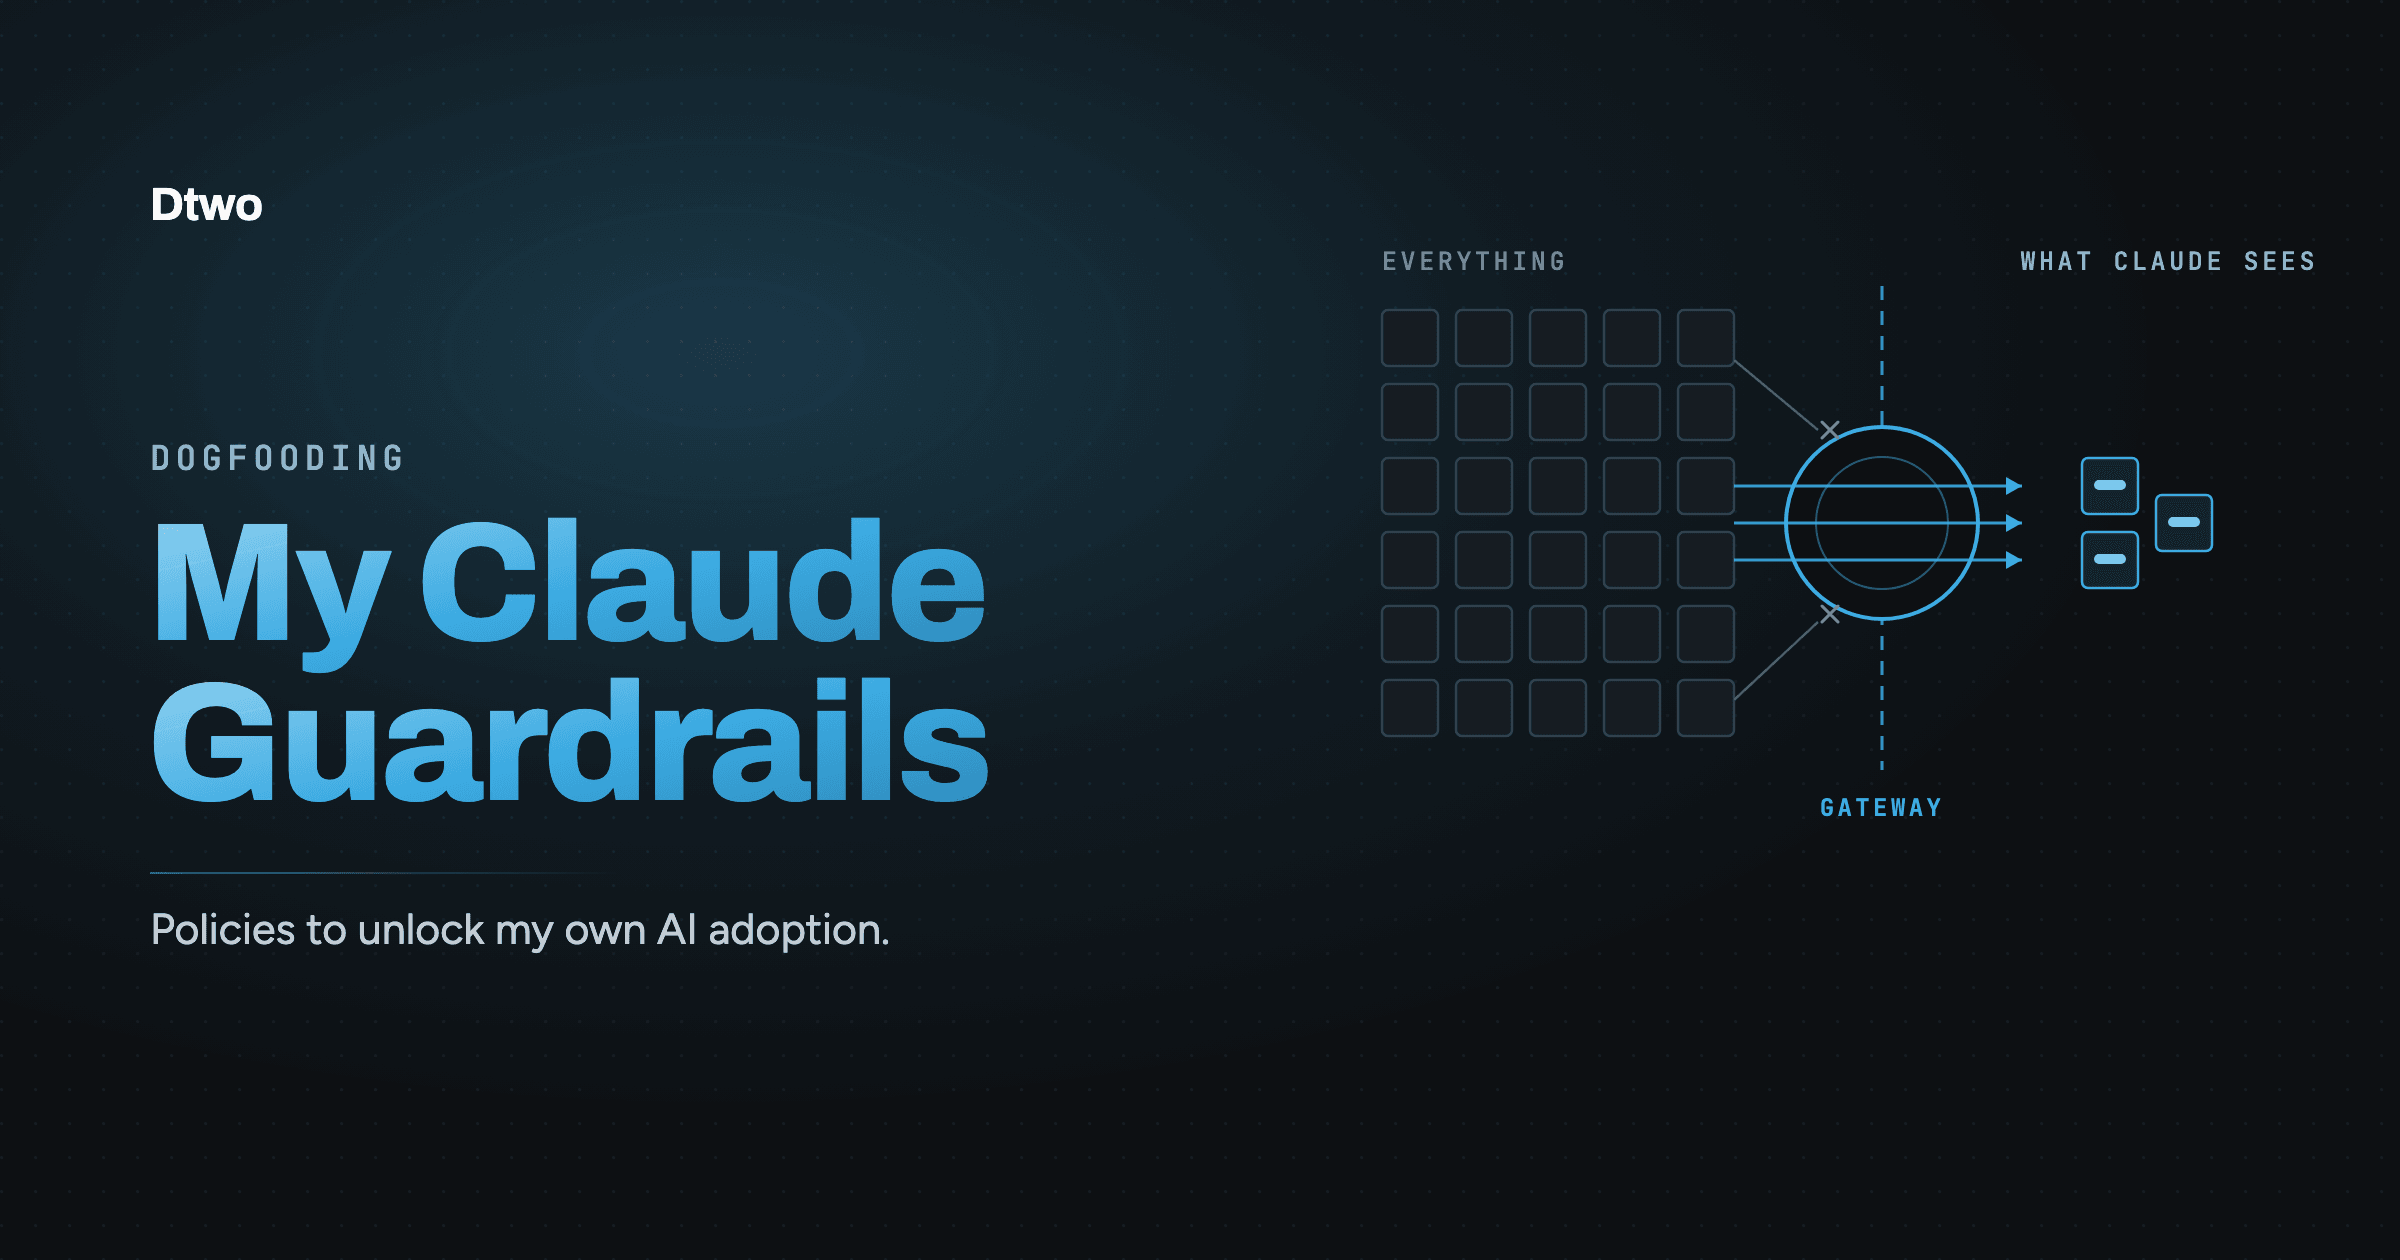
Claude Code can access our internal systems. Here are the guardrails: the policies that decide what my AI agent can actually reach, all published in our policy catalog.
Security3 min read
The risk from AI agents isn't any one system — it's the path between them. Policy guards that path. It's hard to write — so we open-sourced a library of policies.
Security7 min read
Audit worked because people feared getting caught. AI agents don't — so agent security must shift from audit to authorization across every system.
SecurityClaude Cowork8 min read
A practical guide to rolling out Claude Cowork safely: restrict risky access paths, route MCP through a policy layer, and monitor what your agents actually do.
security2 min read
Legacy security controls were built for humans, not AI agents — that's why agentic AI security and governance are breaking. Here's the gap, and how to close it.
productsecurity7 min read
The policy model that closes the gap between what organizations mean and what their controls enforce.